Omada Identity Role and Policy Engine
The user installing Omada Identity Role and Policy Engine (RoPE) must have the following rights and database roles.
| Where | Description |
|---|---|
| Local group settings | The user must be a member of a group that has permission to install software on the system. This is usually Local Administrators. |
| SQL Server roles | To create the database during installation, the user must have the dbcreator server role. |
Create the RoPE database
Omada recommends that you let the installation process create and configure the RoPE database. During installation, the process also enables the read-committed snapshot setting, which RoPE requires.
If you create the database manually before installing the Omada Identity components, enable read-committed snapshot for the RoPE database before using Omada Identity. Without this setting, RoPE cannot process identities correctly.
Multiple instances of RoPE
You can run multiple RoPE service instances on the same server. To increase calculation speed, configure each instance to queue identities in parallel during each cycle.
To install more than one RoPE service, run the following command from a command prompt:
%windir%\Microsoft.NET\Framework\v4.0.30319\installutil /i /ServiceIdx=<index> "C:\Program Files\Omada Identity Suite\Role and Policy Engine\Service\Omada.RoPE.EngineExecutor.exe"
Each installed service must have a unique service index on that server. The ServiceIdx parameter must be an integer. The default RoPE service has the service index 0.
All installed services can use the same binaries and configuration files. To run services with different configuration options, such as the batch size, copy the directory, edit the configuration files, and install the services from their respective directories.
To queue identities across multiple instances, set queueModifiedEachCycle to True in the EngineConfiguration.config file for each RoPE instance.
Install the RoPE service
The following steps explain how to install the RoPE service.
Install RoPE
-
Double-click OIS Role and Policy Engine.exe to launch the Omada Identity RoPE installation wizard, then click Next.
-
Select the destination folder. The default is C:\Program Files\Omada Identity Suite\Role and Policy Engine. To choose a different folder, click Change... and browse to the desired location.
-
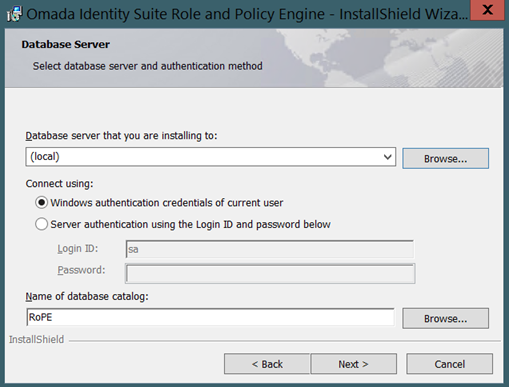
Enter the name of the database server where you are installing the database, then select an authentication method.
In Name of database catalog, specify the database name, or use the default name shown, then click Next.
-
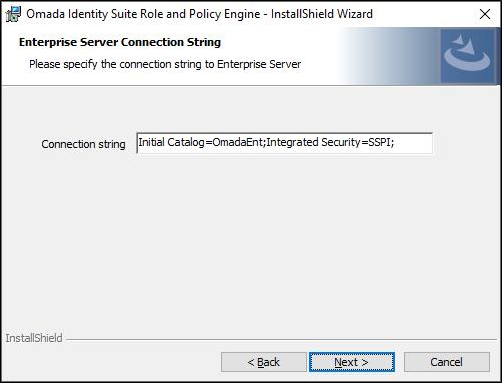
Enter the connection string for the Omada Identity Enterprise Server (ES) database. In Initial Catalog, enter the name of your ES database, which is Omada Identity Suite (OIS) by default.
-
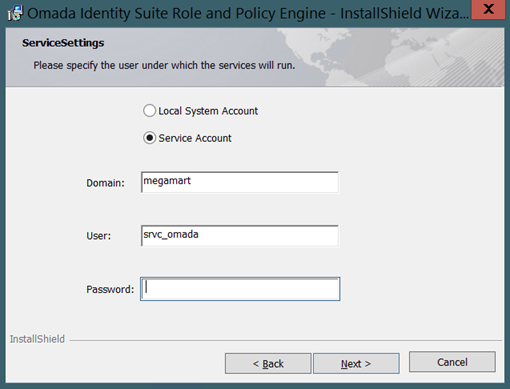
Under Service Account, specify the account that the service will run under, then click Next.
-
Click Install. To make changes, click Back.
-
When the selected program features have been installed, click Finish to complete the installation.
Start the RoPE service
The screenshots in this section are from an earlier version of Omada Identity. Service names and version numbers in your installation may differ.
-
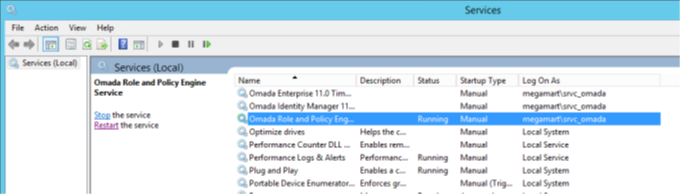
By default, the Omada RoPE Service has a Manual startup type, so you must start it manually. Go to Administrative Tools > Services, and locate Omada RoPE Service.
-
Right-click the service and select Start. The service will run until you restart or shut down the computer.
noteIf you installed multiple RoPE service instances, each instance appears separately in the Services list. Start each one separately.
-
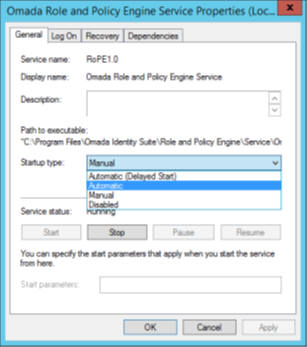
To change the service's startup type, right-click the service and select Properties.
-
On the General tab, select a startup type, such as Automatic instead of Manual, then click OK to save the change.
Grant the service account used by the Omada RoPE service the Log on as a service right in Local Policies and the db_owner role in the RoPE database.
Upgrade the RoPE service
Before installing a new RoPE version to upgrade an existing installation, complete the required preparation steps.
For details, see the Upgrade guide.