Omada Provisioning Service
Omada Provisioning Service (OPS) runs as a Windows service.
Run the service under a service account. If you use a service account, have the account credentials ready before starting the installation.
Database
The OPS installer creates the required database during installation. If you do not want the installer to create it, you can create the database yourself. Do not add any database tables. The installer creates all the required tables.
During installation, the OPS database is configured to enable the snapshot setting. This setting is required for OPS to operate properly.
If you create the OPS database manually, enable both read_committed_snapshot and allow_snapshot_isolation for the database before using Omada Identity.
Namespace reservation
During installation, the OPS installer creates a namespace reservation for http://+:8000/ProvisioningService/Service/ for the service account selected during installation.
If you change the account later, update the namespace reservation manually.
To show the current namespace reservation, run:
netsh http show urlacl http://+:8000/ProvisioningService/Service/
To delete an existing namespace reservation, run:
netsh http delete urlacl http://+:8000/ProvisioningService/Service/
To add a new namespace reservation, run:
netsh http add urlacl http://+:8000/ProvisioningService/Service/ user="domain\user"
If the service runs as Local System Account, use a user of the BUILTIN\ type.
User rights for installing the Omada Provisioning Service
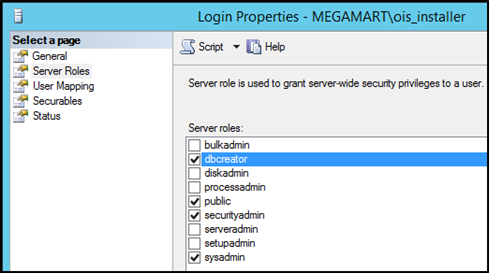
The user installing OPS must have the following rights and database roles.
Local group settings
In Local Group settings, the user must belong to a group that is allowed to install software on the system. This is usually Local Administrators.
SQL Server roles
To create the database during installation, the user must have the dbcreator server role.
If an empty database was created before installation, the user installing the OPS must have the db_owner role for that database.
To install OPS on a SQL Server instance, the installing user must have sysadmin and securityadmin permissions for the service account.
Configure SSL
During installation, the Windows Communication Foundation (WCF) services are configured to use HTTP by default. Omada recommends using the more secure Secure Sockets Layer (SSL) protocol.
To configure SSL:
- Change the service configuration file so that the service uses SSL.
- Update the OPS instance in Enterprise Server (ES).
- Verify that the certificate is correctly linked to the port.
Change the service configuration file
-
Using a text editor, open Omada.OPS.Service.exe.config in the C:\Program Files\Omada Identity Suite\Provisioning Service folder.
-
Comment out or remove the following element:
<service name="Omada.OPS.Service.WCF.Impl.AllWcfServices" behaviorConfiguration="ProvisioningServiceServiceBehaviorSecure"> -
Immediately after the element in step 2, find the following commented-out section and uncomment it:
<service name="Omada.OPS.Service.WCF.Impl.AllWcfServices" behaviorConfiguration="ProvisioningServiceServiceBehaviorSecureHttps">
The default port number is 8001.
Next, update the OPS instance in ES.
Update the OPS instance in ES
-
In the Omada Identity Portal, go to Setup > Administration > Connectivity > OPS Instances.
-
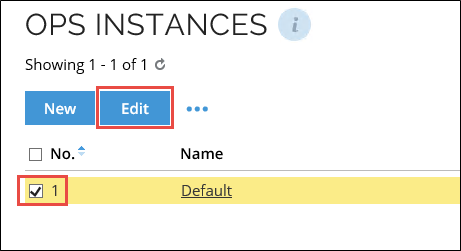
In the OPS Instances view, select the check box next to the default instance, then click Edit.
-
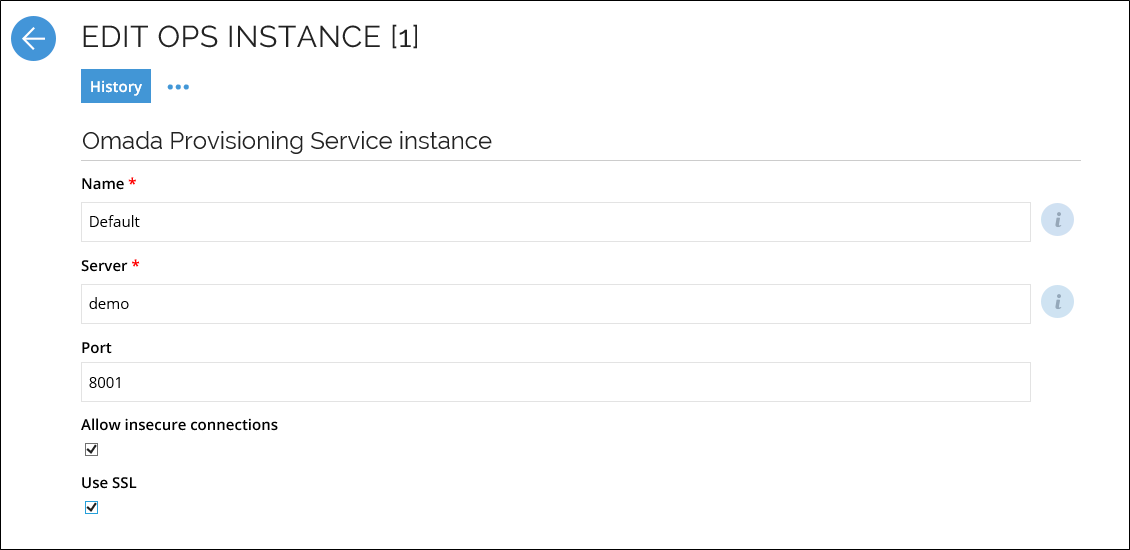
In the Edit OPS Instance view, select the Use SSL check box.
-
In the Port field, change the value to 8001.
noteIn the Server field, specify the server hosting the service.
When using SSL, you cannot specify IP addresses.
Next, verify the connection and confirm that the certificate is correctly linked to the port.
Verify the connection
If you are upgrading OPS from version 12.1 or earlier, add the reservation manually as shown in step 1 of this procedure.
You do not need to perform this step for a clean Omada Identity installation.
-
The installer creates a URL reservation for HTTPS on port 8001. To add the reservation manually, open a command prompt on the OPS server and run the following command. Replace the user value with the account running the OPS service:
netsh http add urlacl url=https://+:8001/ProvisioningService/Service/ user=xxxxx\srvc_omada -
Import your SSL certificate to the server where OPS is installed.
noteMake sure the certificate has a private key and is imported to the following path in the Windows certificate store:
(Local Computer)\Personal\CertificatesOtherwise, you may see this error:
SSL Certificate add failed, Error: 1312 A specified logon session does not exist. It may already have been terminated.To import your certificate with its private key, run the following PowerShell command. Replace the file path with the location where you saved your SSL certificate (.pfx) file. You are prompted for the certificate password:
Import-PfxCertificate -FilePath [c:\mycert.pfx] -CertStoreLocation cert:\LocalMachine\My -Password (Read-Host -AsSecureString -Prompt "Certificate password") -
To get the certificate thumbprint, run the following PowerShell command:
Get-ChildItem -Path cert:\LocalMachine\My\noteCopy or write down the thumbprint. You will need it in the next step.
-
Bind the SSL certificate to the OPS service using the following command. Replace the certhash value with the thumbprint from step 3:
netsh http add sslcert ipport=0.0.0.0:8001 certhash=d32d8ff70fb4c27977fada0ce2d41facddd9c0d9 appid={86521b84-b247-4a15-b698-9d0bcc61e520} -
After completing all the steps in this procedure, restart the OPS service.
Install the Omada Provisioning Service
-
Double-click Omada Provisioning Service.exe to launch the installation wizard. On the welcome screen, click Next.
-
Select the destination folder. By default, this is C:\Program Files\Omada Identity Suite\Provisioning Service. To choose a different folder, click Change... and browse to the desired location. Click Next.
-
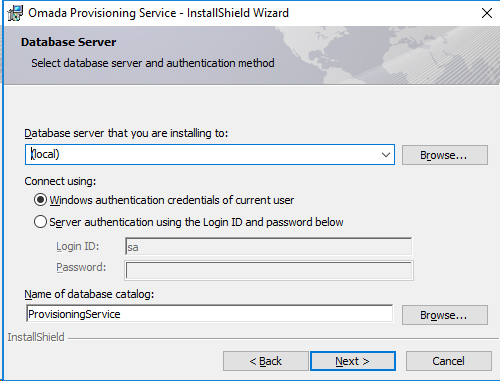
Enter the name of the database server where you are installing the database, then select an authentication method. Omada recommends connecting with Windows authentication credentials of current user.
In Name of database catalog, specify the database name. You can use a manually created, empty database or create a new database. You can also use the default name shown. Click Next.
-
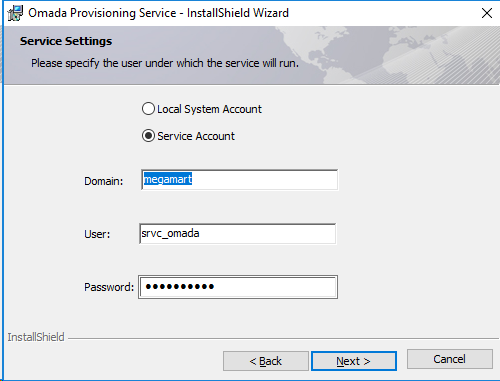
Specify whether to run the service as a Local System Account or a Service Account. Omada recommends using a dedicated service account. If you select Service Account, enter the credentials. The credentials are stored only as part of the Windows service registration.
-
Under Custom Setup, select the features you want to install.
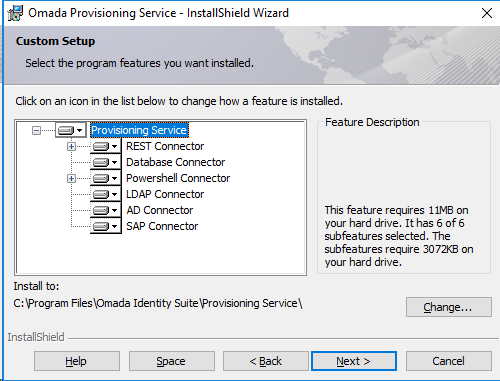
The Provisioning Service feature installs the service, database, and connectors for REST, Database, PowerShell, Lightweight Directory Access Protocol (LDAP), Active Directory (AD), and SAP, if selected.
-
Click Next, then click Install. After the selected features have been installed, click Finish to close the installation wizard.
-
On the server, start OPS in Administrative Tools > Services. The service does not start automatically as part of the installation.
Troubleshooting
Installer displays a warning for the service account
When a warning about the service account appears, click Yes and continue with the installation.
Alternatively, close the installer. Before restarting it, right-click the installer file and select Run as administrator.
Installer does not detect an old version of OPS/ODW and will not upgrade
See the Installer does not detect an old version of OPS/ODW and will not upgrade section.
Unable to start the Omada Provisioning Service
If the OPS does not start, open Event Viewer and look for entries with OPS as the source. Review any errors.
Missing namespace reservation
If you get the following error when starting the service, the namespace reservation is incorrect or missing. See Namespace reservation for information about creating the correct reservation.
HTTP could not register URL http://+:8000/ProvisioningService/service/
The reservation must be made for the account running the service.
Unable to log in to the database
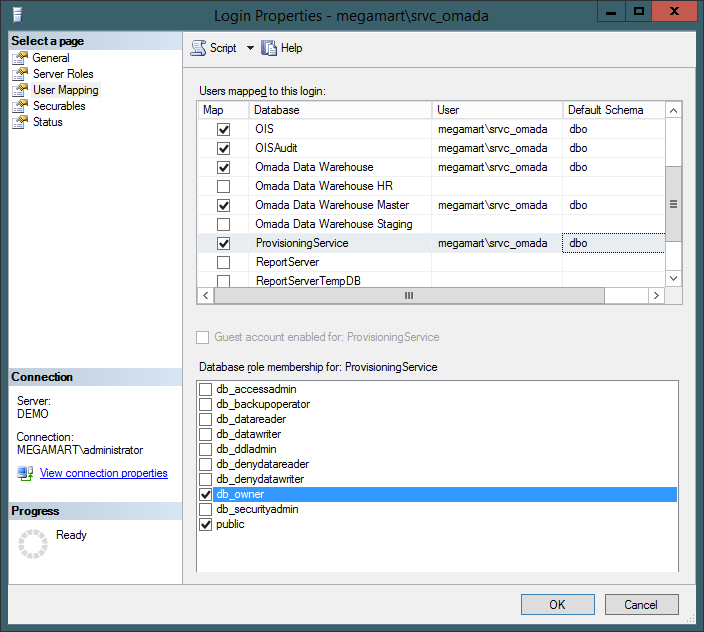
If the service account does not have sufficient rights to open the Provisioning Service database, the following error appears:
Cannot open database "ProvisioningService" requested by the login.
The login failed.

Login failed for user 'megamart\srvc_omada'
Use Microsoft SQL Server Management Studio to grant the service account login db_owner rights to the Provisioning Service database.
Omada DEMO/DEV system: Performance issue
If Omada Identity performs very poorly on VMware virtualization, try disabling Receive Segment Coalescing.
Error installing OPS as a service user
When you run the OPS installer as a service user, the following error may appear:
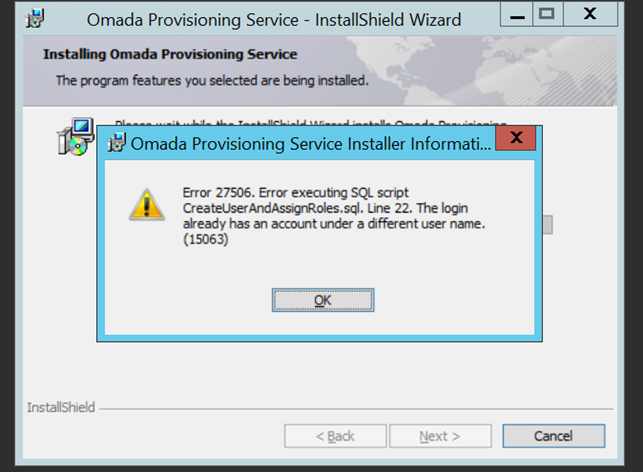
To resolve the issue causing this error:
-
Create the ProvisioningService database. Skip this step if the database already exists.
-
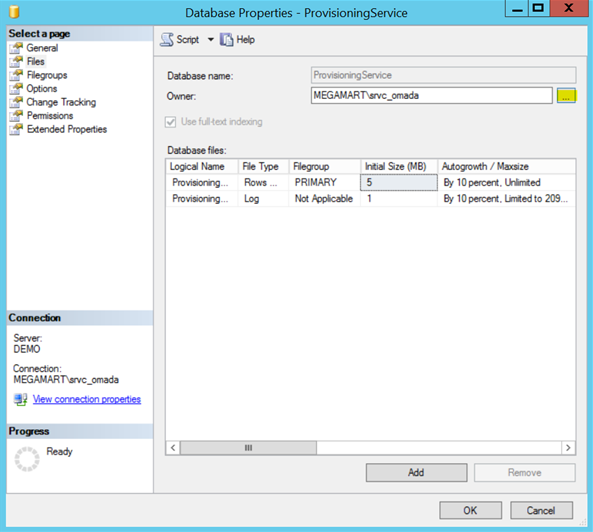
Change the database owner to an account other than the service user.
-
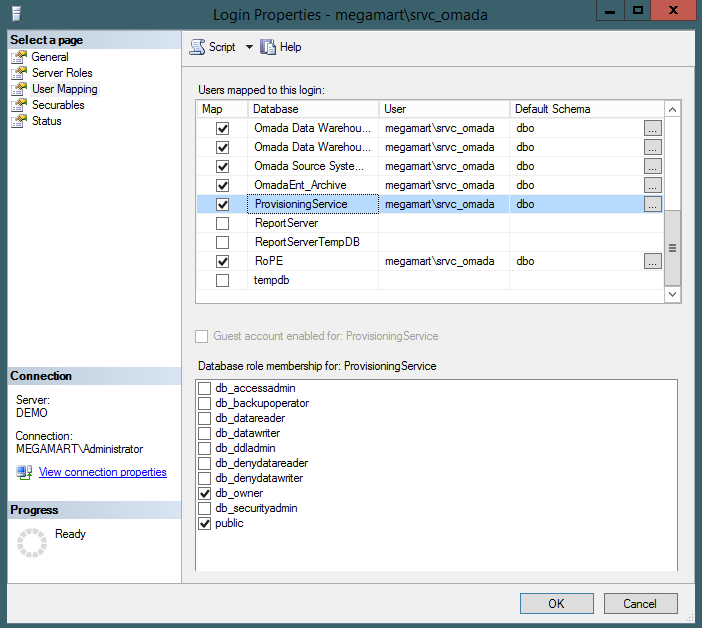
Make sure the service user has db_owner rights for the ProvisioningService database.
-
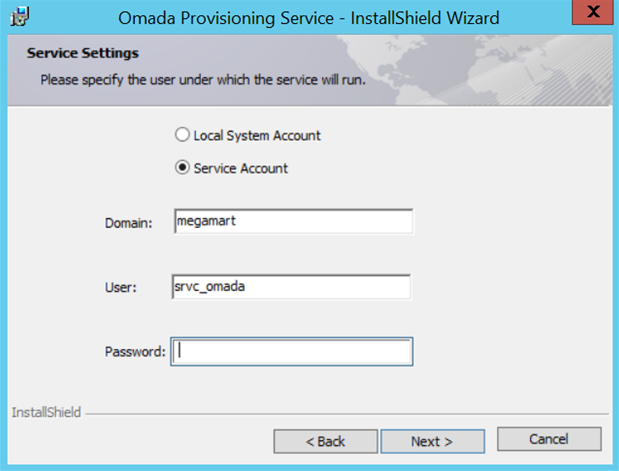
Run the installer again as the service user. This is the user name entered in the User: field during installation.
Omada Identity Timer Service not starting automatically
When setting up a new environment, startup may improve if one or more Omada Identity Windows services run on the same server as SQL Server and depend on the SQL Server Windows service. Use the following commands for the Timer Service, OPS, and Role and Policy Engine (RoPE), as applicable:
sc config OETSVC depend=MSSQLSERVER

sc config "Omada ProvisioningService" depend=MSSQLSERVER

sc config RoPE_0 depend=MSSQLSERVER
The sc command works only in the Windows Command Prompt.
These commands overwrite the existing dependencies of the three services. Before running them, open the Services application, view each service's properties, and note its current dependencies. To retain existing dependencies, add them to the commands above, preceded by a slash.
For example, if the Timer Service depends on the Windows Management Instrumentation (WMI) Performance Adapter service, use this command:
sc config OETSVC depend=MSSQLSERVER/wmiApSrv