Additional security aspects
Some of the security aspects within Omada Identity are relevant for several of the solution's components. Elements such as shared secret or password encryption key are not associated with Enterprise Server (ES) or Omada Provisioning Service (OPS) only, but span across the entire Omada Identity. This page provides an overview of these aspects, and it is relevant for all the components of Omada Identity.
Security aspects relevant to Omada Identity Cloud and on-premises
This section covers security aspects that are relevant for both on-prem and cloud deployments of Omada Identity.
Encryption
Omada Identity uses a PBES2-based encryption method as defined by the JSON Web Encryption (JWE) standard to protect sensitive data. The method is disabled by default. The UseJWE customer setting controls whether it is used and defaults to False.
The JWE uses the following algorithm identifiers:
alg:PBES2-HS512+A256KW.enc:A256GCM.
In PBES2-HS512+A256KW, HS512 identifies HMAC SHA-512 as the pseudorandom function used by PBKDF2. It does not specify or imply a password or key length. The p2c parameter is taken from the PBKDF2 iteration count master setting when the system boots.
The encryption mechanism uses the following components:
-
PBKDF2 with SHA-512 (Password-Based Key Derivation Function 2) as the key derivation function.
ExplanationAn algorithm strengthens passwords by repeatedly hashing them. This process makes it much harder for attackers to guess or brute-force the original password because it slows down every attempt with thousands of hash iterations.
-
AES-256-GCM (A256GCM) as the encryption mode.
ExplanationIt is a modern encryption standard that both protects the confidentiality of data and verifies that it has not been tampered with. It uses a 256-bit key for strong security and includes built-in integrity checks, so if the encrypted data is changed in any way, the decryption process will detect it.
-
A random salt generated for every encryption operation.
ExplanationEven if the same password is used multiple times, the derived encryption key will always be different.
-
A random initialization vector (IV) generated for every encryption operation.
ExplanationEven if the same plaintext is encrypted multiple times with the same key, the ciphertext will always differ.
-
A configurable iteration count to balance performance and security requirements.
ExplanationThe PBKDF2 iteration count master setting allows system administrators to specify the number of iterations for the PBKDF2 key derivation function. The default value is set to 210,000, which aligns with modern security recommendations for PBKDF2 with SHA-512.
For more technical details, see Master settings – Security.
Performance considerationsWhile higher values for the PBKDF2 iteration count can improve security by making brute-force attacks more computationally expensive, they can also impact system performance. To strike the right balance between performance and security, evaluate your security needs and system capabilities when configuring this setting.
Security aspects relevant to Omada Identity (on-premises)
The following sections cover security aspects that are relevant for on-prem deployments of Omada Identity.
Password encryption key
Omada Identity uses a common encryption key, PswEncryptionKey, for all of its main components. This key is used to encrypt sensitive data such as passwords or connection strings.
Key requirements
PswEncryptionKey is a password input to PBKDF2, not a fixed-length encryption key. No specific input length is required. Omada recommends using a randomly generated value with at least 128 bits of entropy. As practical examples, use 32 or more randomly generated alphanumeric characters, or 64 randomly generated hexadecimal characters.
Use only alphanumeric or hexadecimal characters. This avoids XML escaping issues in configuration files and quoting issues when passing the value to StringEncrypter.exe. The value must be identical across all components that use it.
PswEncryptionKey can be stored in several places in Omada Identity. Omada recommends storing the key in the Windows registry under HKEY_LOCAL_MACHINE\SOFTWARE\Omada\Omada Identity Suite, but alternatively, it can be stored in the configuration files for each component: the Web.config file (ES), Omada.OPS.Service.exe.config file (OPS), AppSettings.config file (RoPE), and Omada.OE.Service.config file (timer service).
Immediately after Omada Identity is installed, PswEncryptionKey has the default value DefaultEncryptionKey. This value should be changed as soon as possible after installation, preferably before performing any actions within Omada Identity.
The PswEncryptionKey change must be performed manually in all the places where it is used.
However, PswEncryptionKey can be changed at any later stage, even if you have encrypted data with the default key or your updated PswEncryptionKey.
Add a password encryption key for ES, Omada Data Warehouse (ODW), and RoPE
Omada recommends setting a secret password encryption key so that you do not use the default one. Do this before you enter any credentials that are to be encrypted with this key.
To set up the new password encryption key, add a string value named PswEncryptionKey to the following Windows registry path: HKEY_LOCAL_MACHINE > SOFTWARE > Omada > Omada Identity Suite (OIS).
As an alternative, the key can also be stored in the Web.config, Omada.OPS.Service.exe.config, AppSettings.config, and Omada.OE.Service.config files.
The password encryption key must be set on all servers running ES, ODW, and RoPE. For the corresponding configuration of OPS, see the section Add a password encryption key in the OPS.
For Data Preview Service and Vault Service, the password encryption key must be set in their respective configuration files, not in the Windows registry.
Add a password encryption key in the OPS
Omada recommends setting a secret password encryption key so that you do not use the default one. Do this before you enter any credentials that are to be encrypted with this key.
To do this, enter the new password in Omada.OPS.Service.exe.config.
As an alternative, the key can also be set in the registry as described in the section Add a password encryption key for ES, ODW, and RoPE.
<appSettings>
  <add key="PswEncryptionKey" value="DefaultEncryptionKey"/>
</appSettings>
PswEncryptionKey must be the same in all the places where it is set.
Change PswEncryptionKey after data encryption
Changing PswEncryptionKey after it has been used to encrypt data should be done with caution, as an incorrect update may result in data loss or make Omada Identity unresponsive. To change PswEncryptionKey, follow these steps:
- Ensure that all mail queues are empty (initial password encrypted).
- Ensure that all account provisioning jobs with initial passwords in OPS are finalized.
- Ensure that the account creation has been confirmed by an ODW import, and the account creation email with the initial password has been sent.
- Stop all Omada Identity services on all servers.
- Change
PswEncryptionKeyon all servers, both in the registry and in configuration files. - Re-encrypt previously encrypted database connection strings in the registry and configuration files.
- Re-encrypt application programming interface (API) keys in configuration files.
- Re-encrypt the Azure Service Bus connection string.
- Re-encrypt any encrypted property values on Data Objects. For example, the
INITIALPASSWORDproperty on Identity data objects, if used. - Restart the application pool for Omada Identity on all servers.
- For each onboarded system, visit all tasks where passwords or keys are entered, and re-enter the password.
- Re-encrypt previously encrypted Data Connection connection strings.
Start the Omada Identity services again.
Shared secret authentication
The shared secret is an authentication method for internal process communication between Omada Identity components. It covers the following types of communication:
- Role & Policy Engine to OPS.
- ES to OPS.
- ES to Role & Policy Engine.
This authentication method uses a shared secret. In Omada Identity, the shared secret is the APISharedSecret API key, shared between ES, RoPE, and OPS.
The shared secret is stored in either encrypted or unencrypted form in the configuration files for ES, RoPE, and OPS.
Omada strongly recommends using the StringEncrypter utility to encrypt the shared secret before storing it in the configuration files.
Set up shared secret authentication in ES
To use shared secret authentication, configure it for ES, RoPE, and OPS.
You can configure the authentication by adding the following line with a value for the shared secret to Web.config:
<appSettings>
  <add key="ApiSharedSecret" value=""/>
</appSettings>
The ApiSharedSecret key accepts values encrypted with PswEncryptionKey as well as unencrypted values. If the value is encrypted, Omada strongly advises encrypting ApiSharedSecret with PswEncryptionKey using StringEncrypter. If the value is unencrypted, it cannot contain characters that are illegal in XML configuration files (&, <, >, ", and '). The value must be the same in ES, RoPE, and ODW.
For information on setting up PswEncryptionKey, see the section Add a password encryption key for ES, ODW, and RoPE.
For more information on setting up the shared secret in RoPE, see the section Set up shared secret authentication in RoPE.
Set up shared secret authentication in OPS
To use shared secret authentication, configure it for ES, RoPE, and OPS.
For the Role & Policy Engine, configure authentication by adding the following line with a value for the shared secret to Omada.OPS.Service.exe.config:
<appSettings>
  <add key="ApiSharedSecret" value=""/>
</appSettings>
In addition, change the behavior of the Omada.OPS.Service.WCF.Impl.AllWcfServices service in Omada.OPS.Service.exe.config to support API shared secret.
In behaviorConfiguration, set one of the following service behaviors. When using the shared key, you can use either ProvisioningServiceServiceBehaviorApiSharedSecret or ProvisioningServiceServiceBehaviorApiSharedSecretHttps.
<system.serviceModel>
  <services>
    <service name="Omada.OPS.Service.WCF.Impl.AllWcfServices"
             behaviorConfiguration="ProvisioningServiceServiceBehaviorApiSharedSecret">
The ApiSharedSecret key accepts values encrypted with PswEncryptionKey as well as unencrypted values. If the value is encrypted, Omada strongly advises encrypting ApiSharedSecret with PswEncryptionKey using StringEncrypter. If the value is unencrypted, it cannot contain characters that are illegal in XML configuration files (&, <, >, ", and '). The value must be the same in ES, RoPE, and ODW.
Set up shared secret authentication in RoPE
To use shared secret authentication, configure it for ES, RoPE, and OPS.
For the Role & Policy Engine, configure authentication by adding the following line with a value for the shared secret to AppSettings.config:
<appSettings>
  <add key="ApiSharedSecret" value=""/>
</appSettings>
The ApiSharedSecret key accepts values encrypted with PswEncryptionKey as well as unencrypted values. If the value is encrypted, Omada strongly advises encrypting ApiSharedSecret with PswEncryptionKey using StringEncrypter. If the value is unencrypted, it cannot contain characters that are illegal in XML configuration files (&, <, >, ", and '). The value must be the same in ES, RoPE, and ODW.
StringEncrypter
Omada Identity includes an encryption tool named StringEncrypter, which is installed along with the software. You can use this tool to encrypt any string or part of a string, for example, a password used in a connection string.
You can encrypt a string by running StringEncrypter in a command prompt. The first parameter, PswEncryptionKey, specifies the encryption key. The second parameter specifies the string to encrypt. You can select and copy the result.
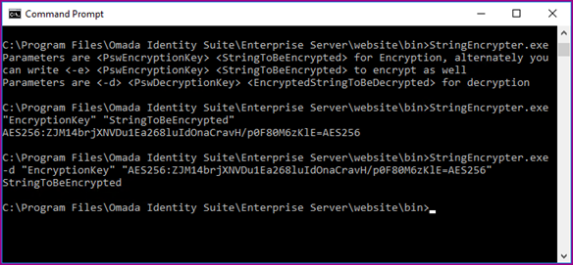
To make sure that the password string is read as a single string, insert quotation marks before and after the password, for example:
StringEncrypter.exe "abc|def" "abc|def".
Do this regardless of whether you have used special characters (for example, &, |, or !).
If you want to encrypt only part of a string, use StringEncrypter on the desired part, and then paste the encrypted part manually into the target string. The encrypted part must include special tags at the start and end. For example, the starting tag is AES256:, and the ending tag is =AES256:
Server=localhost; User Id=AES256:bGUt1APx1lRsvcdwdf9BXQ===AES256;Password=AES256:bGUt1APx1lRsvcdwdf9BXQ===AES256;Database=OIS
StringEncrypter adds these tags automatically.
Library support
The CommonLib Crypto library provides the method EncryptWithPassword, which applies the PBES2 encryption approach with a random salt, random IV, and configurable iteration count.
Caching
Omada Identity applies data caching in selected places to improve the end-user experience.
This means that you must reset Internet Information Services (IIS) when certain configuration data is modified, or wait until the caching period expires and the data is automatically reloaded.
Reset IIS after you have made changes to certain parts of the system’s configuration.
The default caching period is 2 minutes. If needed, you can change the customer setting Configuration Mode to True in your configuration and development environments. This prevents the system from applying caching in selected places.
| Type of data | Cached for | Skips caching in configuration mode |
|---|---|---|
| Views | 2 minutes | Yes |
| Filters (for example, on a view) | 2 minutes | No |
| Context types | 2 minutes | Yes |
| Configuration Objects | 2 minutes | Yes |
| Data Sources | 2 minutes | Yes |
| Data Connections | 2 minutes | Yes |
| XML Schema | 2 minutes | Yes |
| System name of a Data Object Type | 2 minutes | No |
| System name of a Property | 2 minutes | No |
| Data sets used in dashboard charts and KPIs. Run a query specified on a data source definition | Period specified on the data source definition | Yes |
| Members of a user group | 2 minutes | No |
| The identity specified on a user object | 2 minutes | No |
| Menu items | 1 minute | Yes |
Configuration Mode also has an impact in other areas. Avoid setting Configuration Mode to True in production environments because it can affect system performance.